insonl

We open the machine, then build the next one.

software studio — ai, chains, firmware, the hard parts

start a project
insonl

(00) — studio

insonl is a small studio of engineers in Ho Chi Minh City. We revived a rhythm game its publisher shut down, launched a chain, and built the AI that keeps a Vietnamese review site civil. We take hard systems apart, then build new ones that hold up.

the people

  • 0xHideyoshi

    0xHideyoshi

  • 0xThedol

    0xThedol

  • 0xYamamoto

    0xYamamoto

trusted by teams at

  • RMIT University
  • CoinEx
  • VBI
  • Upmesh
  • Xing
  • Codev
  • SQ8

(01) — method

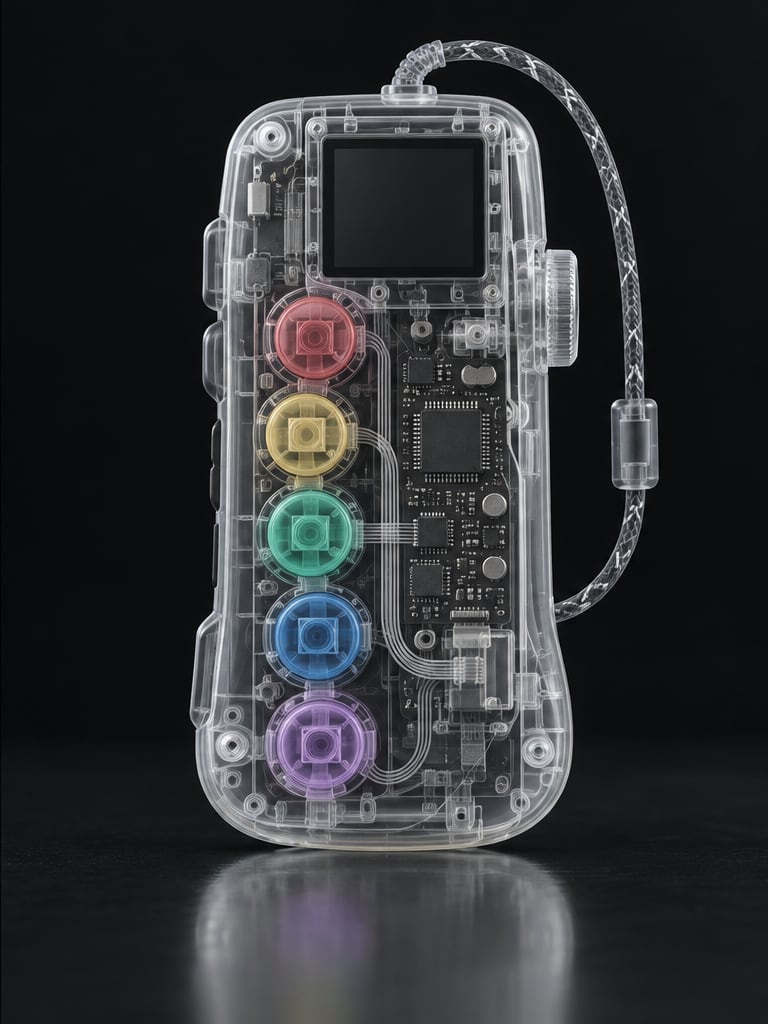
Everything has an inside.

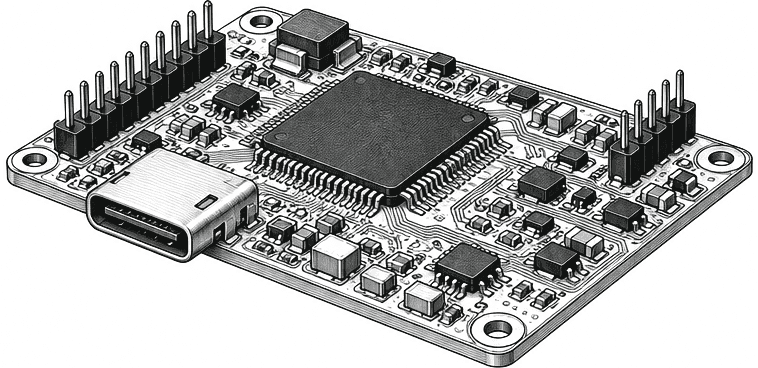
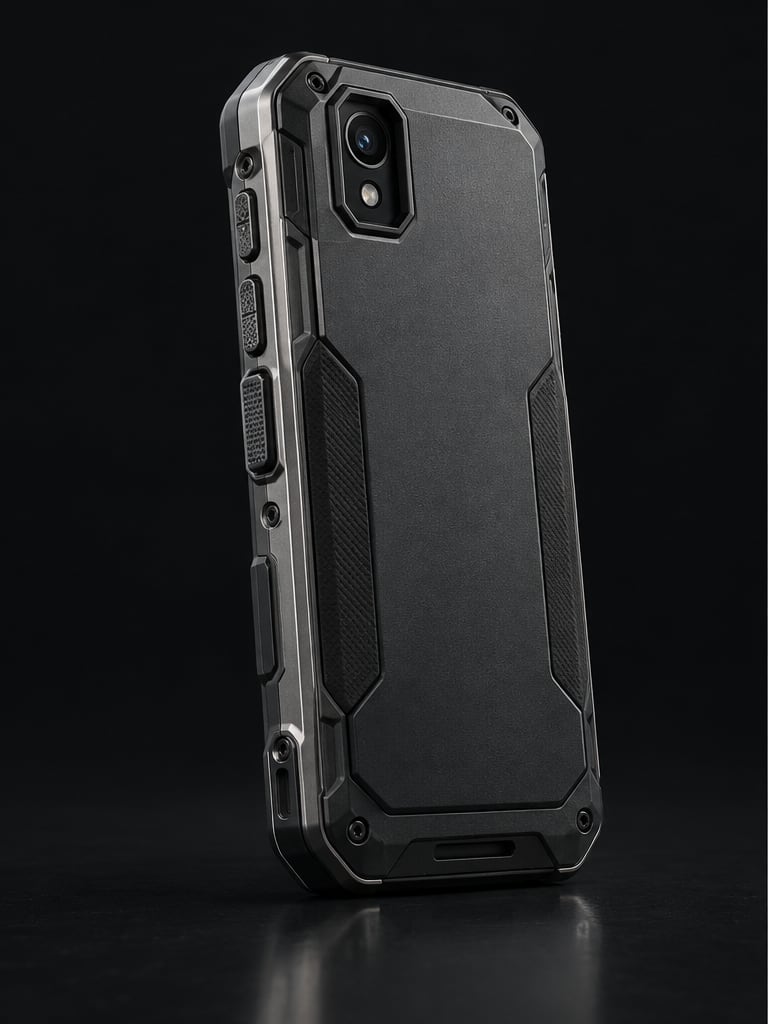
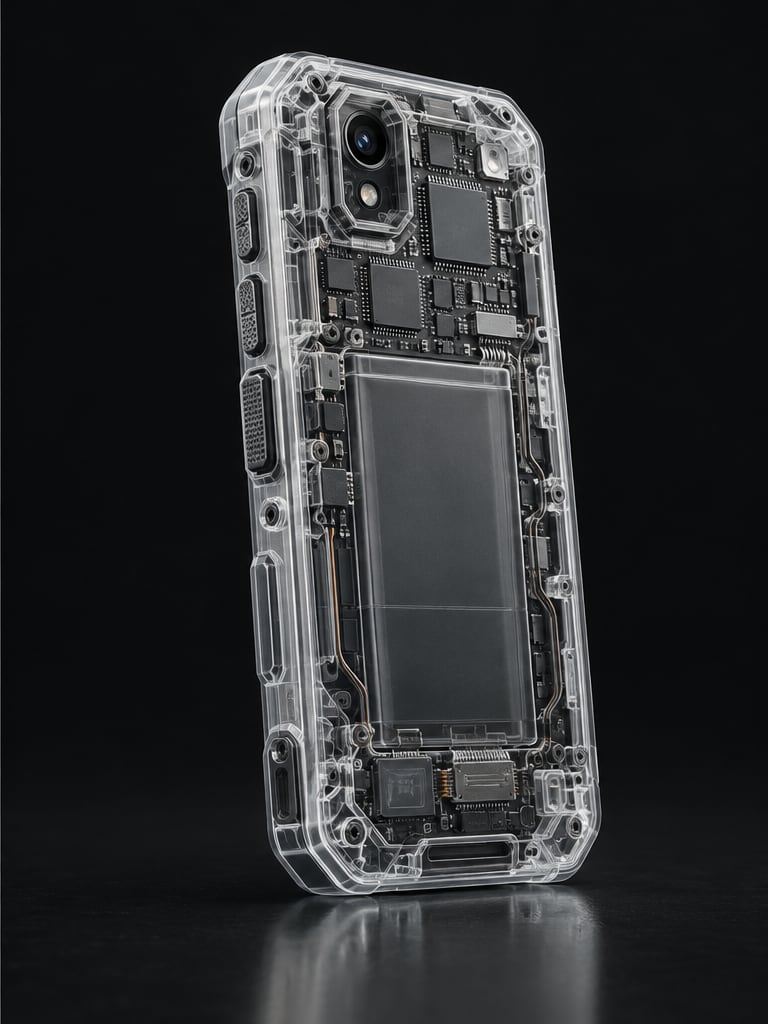
Most studios start from a brief. We start from the box: dump it, map it, read what the last team left behind. Then we build the version that holds up.

scan 000%

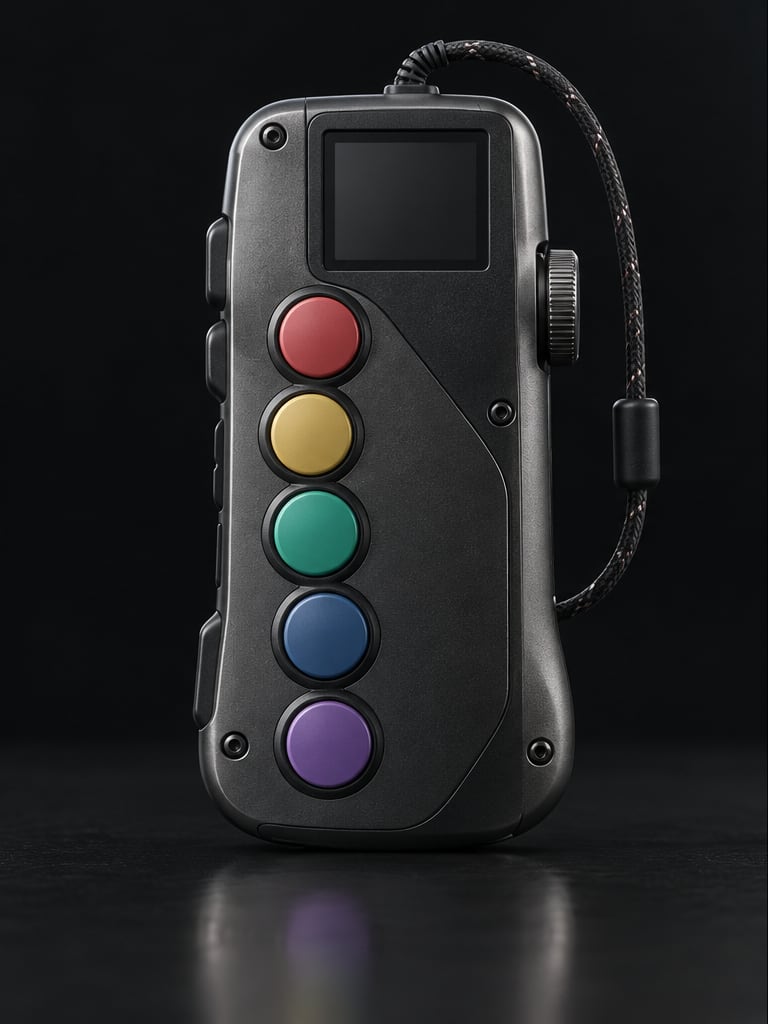
An original handheld rhythm-game device

(02) — practices

Four practices, one team. We pick up the parts other studios hand off.

all services →
01/ 04

Build

Web, mobile & desktop products

Products people use every day, built so the next team can read them. We own the stack end to end, from the first API contract to the store release.

  • Frontend & backend systems↘
  • Native & cross-platform mobile↘
  • PWAs & mini apps↘
  • macOS & Windows apps↘
  • ERP, CRM & BI for operations teams↘
Build — Web, mobile & desktop productshover to inspect
02/ 04

Chain

Web3 & blockchain

We've shipped our own chain and our own mining pool, so we know where the money leaks. Contracts, protocols and the infrastructure under them.

  • Smart contracts & audits↘
  • L2 / L3 chains on Arbitrum Nitro↘
  • DeFi & tokenization↘
  • Mining & validator infrastructure↘
  • Wallets & signing flows↘
Chain — Web3 & blockchainhover to inspect
03/ 04

Machine

AI & embedded systems

Models that run where the work happens: in a moderation queue, on a camera, on a microcontroller with 512 KB to spare.

  • Generative AI & LLM systems↘
  • Computer vision↘
  • AI infrastructure & evals↘
  • Firmware & RTOS↘
  • IoT devices & low-level code↘
Machine — AI & embedded systemshover to inspect
04/ 04

Inside

Security & reverse engineering

We read binaries, protocols and dead servers for a living. It's the same work whether you're hardening a system or bringing one back.

  • Penetration testing↘
  • Blockchain security audits↘
  • Software & hardware RE↘
  • Malware analysis↘
  • Protocol & file-format recovery↘
Inside — Security & reverse engineeringhover to inspect

(03) — how we work

Open.
Map.
Build.
Hold.

01step

Open

We take apart what exists: the code, the infra, the binary nobody has the source for. You get a written teardown before anyone quotes a timeline.

  • + Teardown report
  • + Risk map
  • + Fixed-scope estimate
02step

Map

Architecture, contracts and interfaces on paper first. Cheap to change here, expensive everywhere after.

  • + System design
  • + API & data contracts
  • + Threat model
03step

Build

Weekly increments you can run, not slides about them. Same engineers from the first commit to launch.

  • + Working builds weekly
  • + Test & audit trail
  • + Launch plan
04step

Hold

Launch is where most of the bugs show up. We stay on to monitor, patch and harden until it runs without us.

  • + Monitoring & alerts
  • + Incident runbooks
  • + Handover to your team